AI Ops Audit Toolkit
ready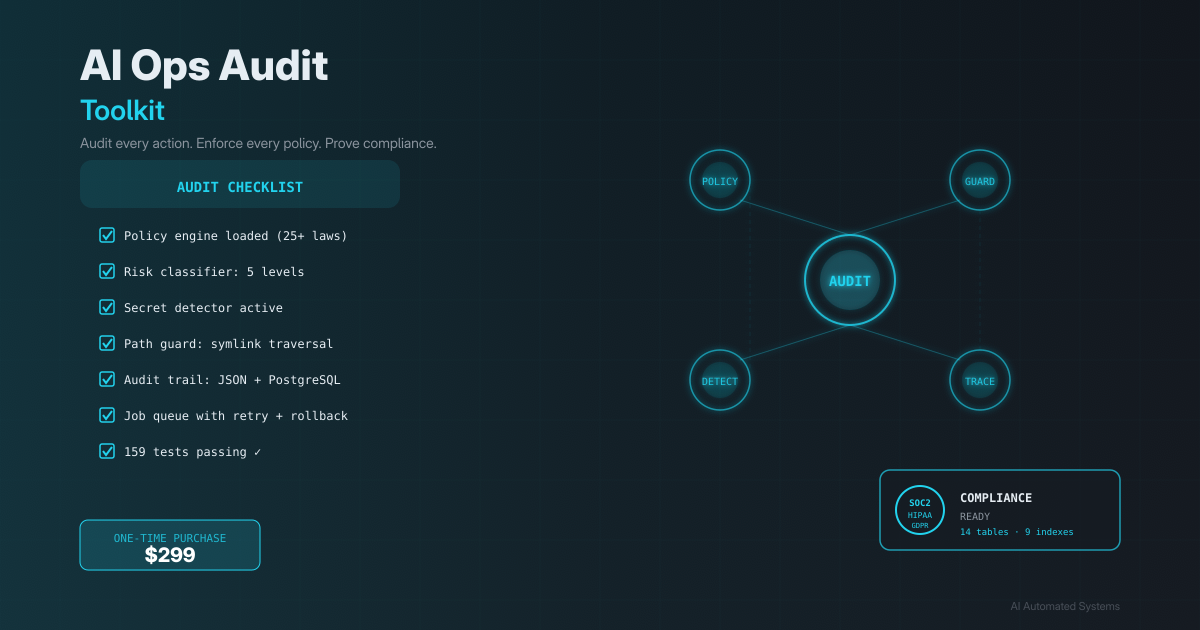
For: Engineering teams running AI agents in production — platform teams, MLOps orgs, and any shop where autonomous agents touch repos, databases, or infrastructure.
Your AI agents push code, run jobs, and touch production — but you have no audit trail, no policy enforcement, no health checks, and no way to prove compliance. One rogue agent action and you're debugging blind.
What you get
A battle-tested governance framework for AI agent operations: policy engine with 25+ pre-built laws, command risk classifier, secret detector, path guard, repo health analyzer, action receipt audit trail, job queue, worker loop, CLI tool, PostgreSQL schema (14 tables), 159 passing tests, and a full compliance checklist. Drop-in Python codebase — adapt to your agent stack in hours.
Preview
What you get
📝 Worksheets & sample data
🧰 Scripts & samples
- src/register_hx370.py
- src/node_registry.py
- src/actions/memory.py
- src/actions/quick_actions.py
- src/actions/__init__.py
- src/actions/action_receipt.py
- src/actions/locking.py
- src/actions/autofix.py
- src/actions/action_pack.py
- src/actions/autonomy.py
- src/intelligence/query.py
- src/intelligence/cross_repo.py
Ready to get started?
Support and assurance
The product page and buyer documents define the delivered materials, setup expectations, and support path. Contact us with the product name and the step that failed; never send credentials or private customer data.
Stripe or Gumroad handles payment
Product-specific terms before purchase
Digital pack or human-led onboarding
Data-minimizing designs where practical
Support path included on every offer